
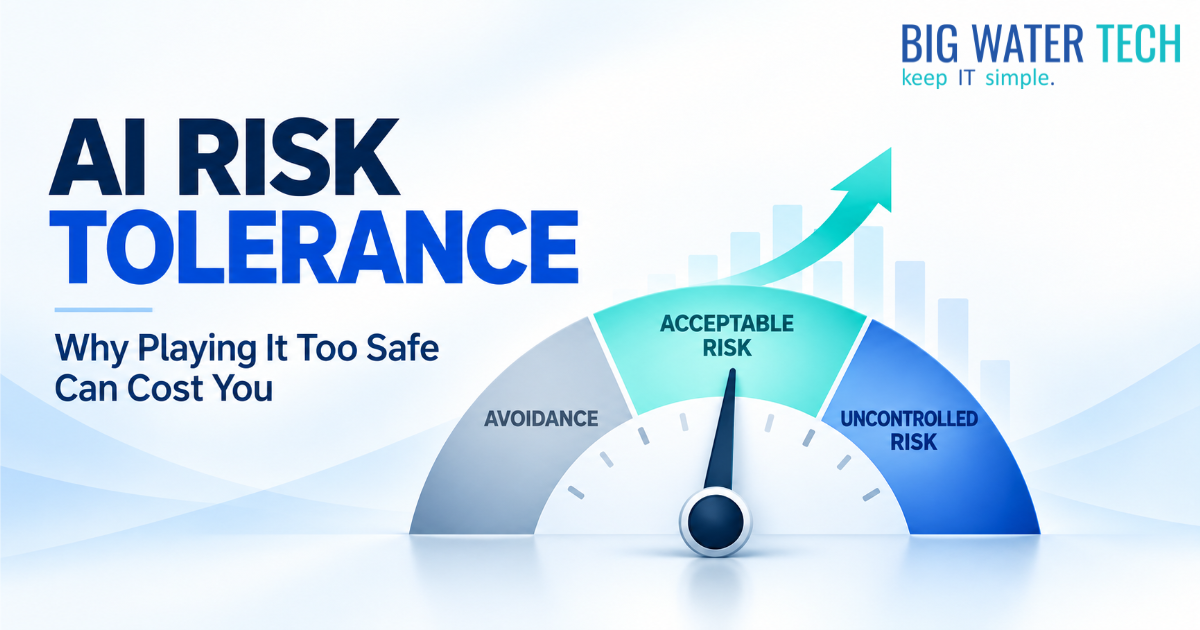
AI Risk Tolerance for Small Business: Why Playing It Too Safe Can Cost You
The safest way to use AI is not to use it.
It may also be one of the riskiest business decisions you make.
Most conversations about artificial intelligence focus on what could go wrong. An employee could paste client information into an unapproved tool. AI could produce a convincing answer that is completely incorrect. A new application could connect to company email, files, or customer data without anyone fully understanding the permissions it was given.
Those are real concerns. Accounting firms, law firms, medical practices, and manufacturers all handle information that should never be casually entered into a public AI platform.
But risk does not exist on only one side of the decision. While your business is avoiding AI, a competitor may be using it to prepare proposals faster, reduce repetitive work, improve customer service, or create additional capacity without immediately adding staff.
Good AI risk management is not about eliminating every possible risk. It is about understanding the downside, recognizing the opportunity, putting reasonable controls in place, and deciding whether the remaining risk is acceptable for your business.
What Is AI Risk Tolerance?
AI risk tolerance is the amount and type of risk a business is willing to accept when using artificial intelligence to pursue a business objective. It considers the potential harm, the potential benefit, the sensitivity of the information involved, and the controls available to reduce exposure.
Every business already has a risk tolerance, even if leadership has never formally documented it. Owners make decisions every day about hiring, equipment, new services, customer contracts, expansion, and technology. None of those decisions comes with a guaranteed outcome.
AI should be treated the same way.
The challenge is that many businesses have not actually decided how much AI risk they are willing to accept. Instead, employees are left with one of two extremes: use whatever helps you get the work done, or do not use AI at all.
Neither is much of a strategy.
What Is Positive Risk?
Risk is usually discussed as something negative. A system might fail, information could be exposed, a deadline might be missed, or an investment may not produce the expected return.
There is another side called positive risk, also known as opportunity risk. Positive risk is the possibility that uncertainty could create a beneficial outcome for the business.
With AI, positive risk could include:
Increasing employee capacity without immediately hiring additional staff
Reducing time spent on repetitive administrative work
Responding to clients or customers faster
Improving consistency across reports, proposals, or internal processes
Helping employees locate and organize information more efficiently
Identifying patterns or opportunities that would otherwise be missed
Making the business easier for clients, customers, and employees to work with
Positive risk does not mean ignoring security or hoping everything works out. It means recognizing that a carefully managed decision can create an upside.
A manufacturer accepts positive risk when it invests in equipment that could increase throughput. An accounting firm accepts it when it hires ahead of tax season. A medical practice accepts it when it introduces a system intended to improve scheduling. A law firm accepts it when it expands into a new practice area.
In each case, leadership considers the possible return, the possible downside, and what can be done to improve the odds of success. AI deserves the same type of business discussion.
What Is Acceptable Risk in AI?
Acceptable AI risk is the remaining level of exposure a business is willing to live with after reasonable safeguards have been applied. It is sometimes called residual risk.
The word "acceptable" matters because no useful technology is completely free of risk. Email creates risk. Cloud services create risk. Remote access creates risk. Even a calculator can create risk if someone enters the wrong number and nobody checks the result.
The goal is not to prove that an AI tool is perfectly safe. The goal is to determine whether the business value justifies the remaining exposure.
For example, using an approved AI platform to summarize public information may create relatively little risk. Entering tax records, legal documents, patient information, employee data, or confidential customer specifications into an unapproved public tool creates a much different situation.
Both examples involve AI, but they are not remotely the same risk.
The Risk of Banning AI Completely
A complete AI ban can feel like the safest policy because it creates a simple answer. Nobody is allowed to use it, so the problem appears to be solved.
In practice, banning AI does not always stop its use. It can push that use underground.
Employees who believe an AI tool will help them finish their work may use free applications or personal accounts without telling anyone. The business then has no reliable way to know which tools are being used, what information is being entered, how long that information is retained, or who has access to it.
The policy reduced the visible risk while potentially increasing the actual risk.
A complete ban can also create business costs that are harder to see:
Employees continue spending hours on work that could be simplified
Client and customer response times remain slower
Competitors learn how to use AI while your organization does not
Employees create unofficial workarounds
The business misses opportunities to improve margins and capacity
Good employees become frustrated with processes that feel unnecessarily slow
Not adopting AI is still a decision. It should be evaluated with the same care as adopting it.
The Risk of Unrestricted AI Use
The opposite extreme creates its own problems. Allowing every employee to select and use any AI application can lead to uncontrolled spending, inconsistent results, security gaps, and a growing collection of tools that nobody is responsible for managing.
The risks may include:
Confidential information entered into personal or free AI accounts
AI tools connected to email, cloud storage, or business systems with excessive permissions
Incorrect output used without human review
Client, patient, employee, or customer information stored by an outside provider
Former employees retaining access to AI accounts or automations
Multiple departments paying for overlapping applications
Business processes becoming dependent on tools leadership does not know exist
"Everyone can use anything" is not an AI strategy. Neither is "nobody can use anything."
The responsible middle is managed risk.
How Should a Small Business Determine Its AI Risk Tolerance?
Start with the business problem, not the AI tool.
Maybe your team spends 20 hours each week gathering information from several systems, copying it into spreadsheets, checking it, and building the same report. Perhaps proposals take too long because someone must search through old documents and manually update information in several places. Maybe employees repeatedly answer the same customer questions or struggle to find procedures stored across different systems.
Once the problem is clear, leadership can evaluate whether AI offers enough potential value to justify the risk.
1. Define the desired business outcome
Be specific about what should improve. "We want to use AI" is not a business objective. "We want to reduce the time required to prepare the weekly production report from eight hours to two" is much more useful.
A clear outcome makes it possible to measure whether the project is working and whether the positive risk is producing a real benefit.
2. Identify the information involved
Determine what the AI tool would need to read, process, create, or store. Public information creates a different risk than client financial records, protected health information, legal documents, employee data, customer specifications, or intellectual property.
If nobody can explain what information the tool will access, the business is not ready to approve it.
3. Consider what could go wrong
Look beyond cybersecurity. An AI tool can create operational, financial, legal, compliance, reputational, and client-service risks.
Could it produce an inaccurate answer? Could an employee send that answer to a client without checking it? Could sensitive information be retained by the provider? Could an automation continue running after the employee who created it leaves?
The purpose is not to create fear. It is to understand the decision before making it.
4. Put reasonable controls in place
The right controls will depend on the use case, but they may include:
A short list of approved AI tools
Business-managed accounts instead of personal accounts
Clear rules about which information may never be entered
Appropriate identity, access, and multifactor authentication controls
Human review before AI output is used externally
Vendor and contract review
Employee training based on actual job responsibilities
Logging, monitoring, and a process for removing access
A way to suspend AI access if a security or operational problem occurs
Controls should reduce risk without making the approved process so difficult that employees return to unapproved tools.
5. Decide whether the remaining risk is acceptable
After the controls are applied, some risk will remain. Leadership must decide whether that risk is reasonable compared with the potential business benefit.
That decision should be documented. It should also have an owner and a date for review because AI tools, business processes, and risk levels change.
Examples of Low, Moderate, and High-Risk AI Use Cases
The same AI application can create different levels of risk depending on how it is used.
AI use case | Potential positive risk | Possible downside | Reasonable controls | Typical risk level |
|---|---|---|---|---|
Summarizing public research | Saves research time | Inaccurate or incomplete information | Verify sources and important facts | Lower |
Drafting internal training material | Creates content faster | Incorrect or inconsistent guidance | Subject-matter review before use | Lower to moderate |
Creating a first draft of a client email | Improves response time | Wrong tone, facts, or confidential details | Approved tool and human approval | Moderate |
Summarizing internal meeting notes | Reduces administrative work | Sensitive information stored externally | Approved platform, access controls, retention rules | Moderate |
Analyzing operational or production data | Identifies trends and saves analysis time | Confidential data exposure or incorrect conclusions | Data controls, approved environment, human validation | Moderate to high |
Processing tax, legal, patient, or regulated data | May create significant efficiency | Privacy, contractual, legal, and compliance exposure | Formal review, strict access controls, approved platform, documented oversight | High |
Making financial, legal, employment, or patient decisions without review | Faster decisions | Significant harm from inaccurate or biased output | Require qualified human decision-making | Usually unacceptable |
These are starting points, not universal ratings. A use case that is acceptable for one organization may be unacceptable for another because the data, contracts, regulations, clients, and controls are different.
What Does AI Risk Tolerance Look Like by Industry?
Accounting firms
Accounting firms may find positive risk in reducing the manual work required to organize public research, create internal checklists, prepare first drafts, or summarize non-sensitive information. The risk rises quickly when tax records, payroll information, financial statements, or personally identifiable information are involved.
An accounting firm's acceptable use policy should reflect its obligation to protect client financial data and its need to maintain client trust.
Law firms
Law firms may use AI to organize information, improve internal workflows, or help prepare early drafts. However, confidentiality, accuracy, privilege, and client requirements must be considered before information is entered into any AI system.
Human review is especially important when AI output could influence legal advice, filings, contracts, or client communication.
Medical practices
Medical practices may identify opportunities in scheduling, administrative communication, staff training, and other non-clinical processes. Any use involving protected health information requires much closer review of privacy, security, access, retention, and vendor responsibilities.
The potential efficiency does not remove the practice's responsibility to protect patient information.
Manufacturers
Manufacturers may use AI to document processes, analyze non-sensitive operational information, improve quoting, organize maintenance knowledge, or identify production patterns. The risk changes when the tool can access customer specifications, proprietary processes, supplier agreements, employee information, or controlled data.
Customer contracts and security questionnaires may also place limits on how information can be processed, even when a particular law does not.
Who Should Decide What AI Risk Is Acceptable?
AI risk tolerance is a leadership decision.
Your IT provider should help explain the technology, permissions, integrations, security controls, and potential data exposure. Legal, compliance, human resources, and insurance advisors may need to contribute depending on the use case.
But those advisors should not decide the business's risk tolerance on their own.
The owner, managing partner, or leadership team understands the importance of client trust, employee capacity, production schedules, margins, contractual obligations, and growth plans. Leadership must compare the potential downside with the potential positive risk and decide whether the opportunity is worth pursuing.
This does not require a large committee for every small experiment. It requires clear decision rights. Someone should have the authority to approve a use case, someone should own the controls, and someone should know when the decision needs to be reviewed.
How Often Should AI Risk Decisions Be Reviewed?
AI risk decisions should be reviewed when the tool, data, integration, business process, or regulatory obligation changes. They should also be included in a regular technology and risk review instead of being treated as one-time approvals.
A tool initially approved for public research may later be connected to company files. An application that began with three users may spread across the entire business. A vendor may change its terms, retention practices, or security features. Each of those changes can alter the acceptable risk calculation.
At minimum, leadership should know:
Which AI tools are approved
Who is using them
What business purposes they support
What information they can access
Who owns each use case
Whether the expected business benefit is actually being achieved
What would cause access to be limited or stopped
Frequently Asked Questions About AI Risk Tolerance
Should a small business ban AI?
A complete AI ban may be appropriate for specific tools, data types, or activities, but a blanket ban can push employees toward unapproved tools and cause the business to miss legitimate opportunities. A better approach is to define approved uses, prohibited information, required controls, and human-review expectations.
What is the difference between risk tolerance and acceptable risk?
Risk tolerance describes how much and what type of uncertainty the business is generally willing to accept. Acceptable risk is the specific level of exposure leadership agrees to retain for a particular decision or use case after safeguards are applied.
What is positive risk in AI?
Positive risk is the possibility that using AI could create a beneficial business outcome, such as greater capacity, faster service, lower administrative effort, improved consistency, or a competitive advantage. It is also called opportunity risk.
Who owns AI risk in a small business?
Leadership owns the decision about whether an AI risk is acceptable. IT, security, legal, compliance, human resources, and insurance advisors can provide important information, but the owner or leadership team must balance the potential harm against the expected business benefit.
What information should never be entered into a public AI tool?
Unless the business has specifically approved the tool and use case, employees should avoid entering confidential client information, patient information, tax records, legal documents, passwords, employee records, financial account information, proprietary processes, customer specifications, or other regulated and contractually protected data.
How can a business begin using AI responsibly?
Start with a specific, lower-risk business problem. Choose an approved tool, limit the information it can access, require human review, assign an owner, measure the result, and expand only after the business understands both the benefit and the remaining risk.
Good Risk Management Should Help the Business Move Forward
Risk management should not become a department of "no." Its purpose is to help leadership make better decisions with a clearer understanding of what could happen.
The businesses that benefit most from AI will not necessarily be the ones that adopt every new tool first. They will be the ones that identify where AI can create real value, understand their risk tolerance, establish clear boundaries, and deliberately pursue the positive risks that support their goals.
The right question is not, "How do we eliminate the risk of AI?"
It is, "What level of risk are we willing to accept so we can continue to grow and remain competitive?"
That is a much more useful conversation.

Ready For A No-Nonsense Approach To IT?
Hire us to set your IT strategy up for sustainable success.
Learn about our proven No-Nonsense approach.
Get an IT roadmap designed specifically for you.
Fearlessly grow your business.
Get in Touch with us!
Call us at (248) 220-7714 or or fill out the form below.
Categories
Featured Posts
AI Risk Tolerance for Small Business: Why Playing It Too Safe Can Cost You
The safest way to use AI is not to use it.
It may also be one of the riskiest business decisions you make.
Most conversations about artificial intelligence focus on what could go wrong. An employee could paste client information into an unapproved tool. AI could produce a convincing answer that is completely incorrect. A new application could connect to company email, files, or customer data without anyone fully understanding the permissions it was given.
Those are real concerns. Accounting firms, law firms, medical practices, and manufacturers all handle information that should never be casually entered into a public AI platform.
But risk does not exist on only one side of the decision. While your business is avoiding AI, a competitor may be using it to prepare proposals faster, reduce repetitive work, improve customer service, or create additional capacity without immediately adding staff.
Good AI risk management is not about eliminating every possible risk. It is about understanding the downside, recognizing the opportunity, putting reasonable controls in place, and deciding whether the remaining risk is acceptable for your business.
What Is AI Risk Tolerance?
AI risk tolerance is the amount and type of risk a business is willing to accept when using artificial intelligence to pursue a business objective. It considers the potential harm, the potential benefit, the sensitivity of the information involved, and the controls available to reduce exposure.
Every business already has a risk tolerance, even if leadership has never formally documented it. Owners make decisions every day about hiring, equipment, new services, customer contracts, expansion, and technology. None of those decisions comes with a guaranteed outcome.
AI should be treated the same way.
The challenge is that many businesses have not actually decided how much AI risk they are willing to accept. Instead, employees are left with one of two extremes: use whatever helps you get the work done, or do not use AI at all.
Neither is much of a strategy.
What Is Positive Risk?
Risk is usually discussed as something negative. A system might fail, information could be exposed, a deadline might be missed, or an investment may not produce the expected return.
There is another side called positive risk, also known as opportunity risk. Positive risk is the possibility that uncertainty could create a beneficial outcome for the business.
With AI, positive risk could include:
Increasing employee capacity without immediately hiring additional staff
Reducing time spent on repetitive administrative work
Responding to clients or customers faster
Improving consistency across reports, proposals, or internal processes
Helping employees locate and organize information more efficiently
Identifying patterns or opportunities that would otherwise be missed
Making the business easier for clients, customers, and employees to work with
Positive risk does not mean ignoring security or hoping everything works out. It means recognizing that a carefully managed decision can create an upside.
A manufacturer accepts positive risk when it invests in equipment that could increase throughput. An accounting firm accepts it when it hires ahead of tax season. A medical practice accepts it when it introduces a system intended to improve scheduling. A law firm accepts it when it expands into a new practice area.
In each case, leadership considers the possible return, the possible downside, and what can be done to improve the odds of success. AI deserves the same type of business discussion.
What Is Acceptable Risk in AI?
Acceptable AI risk is the remaining level of exposure a business is willing to live with after reasonable safeguards have been applied. It is sometimes called residual risk.
The word "acceptable" matters because no useful technology is completely free of risk. Email creates risk. Cloud services create risk. Remote access creates risk. Even a calculator can create risk if someone enters the wrong number and nobody checks the result.
The goal is not to prove that an AI tool is perfectly safe. The goal is to determine whether the business value justifies the remaining exposure.
For example, using an approved AI platform to summarize public information may create relatively little risk. Entering tax records, legal documents, patient information, employee data, or confidential customer specifications into an unapproved public tool creates a much different situation.
Both examples involve AI, but they are not remotely the same risk.
The Risk of Banning AI Completely
A complete AI ban can feel like the safest policy because it creates a simple answer. Nobody is allowed to use it, so the problem appears to be solved.
In practice, banning AI does not always stop its use. It can push that use underground.
Employees who believe an AI tool will help them finish their work may use free applications or personal accounts without telling anyone. The business then has no reliable way to know which tools are being used, what information is being entered, how long that information is retained, or who has access to it.
The policy reduced the visible risk while potentially increasing the actual risk.
A complete ban can also create business costs that are harder to see:
Employees continue spending hours on work that could be simplified
Client and customer response times remain slower
Competitors learn how to use AI while your organization does not
Employees create unofficial workarounds
The business misses opportunities to improve margins and capacity
Good employees become frustrated with processes that feel unnecessarily slow
Not adopting AI is still a decision. It should be evaluated with the same care as adopting it.
The Risk of Unrestricted AI Use
The opposite extreme creates its own problems. Allowing every employee to select and use any AI application can lead to uncontrolled spending, inconsistent results, security gaps, and a growing collection of tools that nobody is responsible for managing.
The risks may include:
Confidential information entered into personal or free AI accounts
AI tools connected to email, cloud storage, or business systems with excessive permissions
Incorrect output used without human review
Client, patient, employee, or customer information stored by an outside provider
Former employees retaining access to AI accounts or automations
Multiple departments paying for overlapping applications
Business processes becoming dependent on tools leadership does not know exist
"Everyone can use anything" is not an AI strategy. Neither is "nobody can use anything."
The responsible middle is managed risk.
How Should a Small Business Determine Its AI Risk Tolerance?
Start with the business problem, not the AI tool.
Maybe your team spends 20 hours each week gathering information from several systems, copying it into spreadsheets, checking it, and building the same report. Perhaps proposals take too long because someone must search through old documents and manually update information in several places. Maybe employees repeatedly answer the same customer questions or struggle to find procedures stored across different systems.
Once the problem is clear, leadership can evaluate whether AI offers enough potential value to justify the risk.
1. Define the desired business outcome
Be specific about what should improve. "We want to use AI" is not a business objective. "We want to reduce the time required to prepare the weekly production report from eight hours to two" is much more useful.
A clear outcome makes it possible to measure whether the project is working and whether the positive risk is producing a real benefit.
2. Identify the information involved
Determine what the AI tool would need to read, process, create, or store. Public information creates a different risk than client financial records, protected health information, legal documents, employee data, customer specifications, or intellectual property.
If nobody can explain what information the tool will access, the business is not ready to approve it.
3. Consider what could go wrong
Look beyond cybersecurity. An AI tool can create operational, financial, legal, compliance, reputational, and client-service risks.
Could it produce an inaccurate answer? Could an employee send that answer to a client without checking it? Could sensitive information be retained by the provider? Could an automation continue running after the employee who created it leaves?
The purpose is not to create fear. It is to understand the decision before making it.
4. Put reasonable controls in place
The right controls will depend on the use case, but they may include:
A short list of approved AI tools
Business-managed accounts instead of personal accounts
Clear rules about which information may never be entered
Appropriate identity, access, and multifactor authentication controls
Human review before AI output is used externally
Vendor and contract review
Employee training based on actual job responsibilities
Logging, monitoring, and a process for removing access
A way to suspend AI access if a security or operational problem occurs
Controls should reduce risk without making the approved process so difficult that employees return to unapproved tools.
5. Decide whether the remaining risk is acceptable
After the controls are applied, some risk will remain. Leadership must decide whether that risk is reasonable compared with the potential business benefit.
That decision should be documented. It should also have an owner and a date for review because AI tools, business processes, and risk levels change.
Examples of Low, Moderate, and High-Risk AI Use Cases
The same AI application can create different levels of risk depending on how it is used.
AI use case | Potential positive risk | Possible downside | Reasonable controls | Typical risk level |
|---|---|---|---|---|
Summarizing public research | Saves research time | Inaccurate or incomplete information | Verify sources and important facts | Lower |
Drafting internal training material | Creates content faster | Incorrect or inconsistent guidance | Subject-matter review before use | Lower to moderate |
Creating a first draft of a client email | Improves response time | Wrong tone, facts, or confidential details | Approved tool and human approval | Moderate |
Summarizing internal meeting notes | Reduces administrative work | Sensitive information stored externally | Approved platform, access controls, retention rules | Moderate |
Analyzing operational or production data | Identifies trends and saves analysis time | Confidential data exposure or incorrect conclusions | Data controls, approved environment, human validation | Moderate to high |
Processing tax, legal, patient, or regulated data | May create significant efficiency | Privacy, contractual, legal, and compliance exposure | Formal review, strict access controls, approved platform, documented oversight | High |
Making financial, legal, employment, or patient decisions without review | Faster decisions | Significant harm from inaccurate or biased output | Require qualified human decision-making | Usually unacceptable |
These are starting points, not universal ratings. A use case that is acceptable for one organization may be unacceptable for another because the data, contracts, regulations, clients, and controls are different.
What Does AI Risk Tolerance Look Like by Industry?
Accounting firms
Accounting firms may find positive risk in reducing the manual work required to organize public research, create internal checklists, prepare first drafts, or summarize non-sensitive information. The risk rises quickly when tax records, payroll information, financial statements, or personally identifiable information are involved.
An accounting firm's acceptable use policy should reflect its obligation to protect client financial data and its need to maintain client trust.
Law firms
Law firms may use AI to organize information, improve internal workflows, or help prepare early drafts. However, confidentiality, accuracy, privilege, and client requirements must be considered before information is entered into any AI system.
Human review is especially important when AI output could influence legal advice, filings, contracts, or client communication.
Medical practices
Medical practices may identify opportunities in scheduling, administrative communication, staff training, and other non-clinical processes. Any use involving protected health information requires much closer review of privacy, security, access, retention, and vendor responsibilities.
The potential efficiency does not remove the practice's responsibility to protect patient information.
Manufacturers
Manufacturers may use AI to document processes, analyze non-sensitive operational information, improve quoting, organize maintenance knowledge, or identify production patterns. The risk changes when the tool can access customer specifications, proprietary processes, supplier agreements, employee information, or controlled data.
Customer contracts and security questionnaires may also place limits on how information can be processed, even when a particular law does not.
Who Should Decide What AI Risk Is Acceptable?
AI risk tolerance is a leadership decision.
Your IT provider should help explain the technology, permissions, integrations, security controls, and potential data exposure. Legal, compliance, human resources, and insurance advisors may need to contribute depending on the use case.
But those advisors should not decide the business's risk tolerance on their own.
The owner, managing partner, or leadership team understands the importance of client trust, employee capacity, production schedules, margins, contractual obligations, and growth plans. Leadership must compare the potential downside with the potential positive risk and decide whether the opportunity is worth pursuing.
This does not require a large committee for every small experiment. It requires clear decision rights. Someone should have the authority to approve a use case, someone should own the controls, and someone should know when the decision needs to be reviewed.
How Often Should AI Risk Decisions Be Reviewed?
AI risk decisions should be reviewed when the tool, data, integration, business process, or regulatory obligation changes. They should also be included in a regular technology and risk review instead of being treated as one-time approvals.
A tool initially approved for public research may later be connected to company files. An application that began with three users may spread across the entire business. A vendor may change its terms, retention practices, or security features. Each of those changes can alter the acceptable risk calculation.
At minimum, leadership should know:
Which AI tools are approved
Who is using them
What business purposes they support
What information they can access
Who owns each use case
Whether the expected business benefit is actually being achieved
What would cause access to be limited or stopped
Frequently Asked Questions About AI Risk Tolerance
Should a small business ban AI?
A complete AI ban may be appropriate for specific tools, data types, or activities, but a blanket ban can push employees toward unapproved tools and cause the business to miss legitimate opportunities. A better approach is to define approved uses, prohibited information, required controls, and human-review expectations.
What is the difference between risk tolerance and acceptable risk?
Risk tolerance describes how much and what type of uncertainty the business is generally willing to accept. Acceptable risk is the specific level of exposure leadership agrees to retain for a particular decision or use case after safeguards are applied.
What is positive risk in AI?
Positive risk is the possibility that using AI could create a beneficial business outcome, such as greater capacity, faster service, lower administrative effort, improved consistency, or a competitive advantage. It is also called opportunity risk.
Who owns AI risk in a small business?
Leadership owns the decision about whether an AI risk is acceptable. IT, security, legal, compliance, human resources, and insurance advisors can provide important information, but the owner or leadership team must balance the potential harm against the expected business benefit.
What information should never be entered into a public AI tool?
Unless the business has specifically approved the tool and use case, employees should avoid entering confidential client information, patient information, tax records, legal documents, passwords, employee records, financial account information, proprietary processes, customer specifications, or other regulated and contractually protected data.
How can a business begin using AI responsibly?
Start with a specific, lower-risk business problem. Choose an approved tool, limit the information it can access, require human review, assign an owner, measure the result, and expand only after the business understands both the benefit and the remaining risk.
Good Risk Management Should Help the Business Move Forward
Risk management should not become a department of "no." Its purpose is to help leadership make better decisions with a clearer understanding of what could happen.
The businesses that benefit most from AI will not necessarily be the ones that adopt every new tool first. They will be the ones that identify where AI can create real value, understand their risk tolerance, establish clear boundaries, and deliberately pursue the positive risks that support their goals.
The right question is not, "How do we eliminate the risk of AI?"
It is, "What level of risk are we willing to accept so we can continue to grow and remain competitive?"
That is a much more useful conversation.
Enroll in Our Email Course
Learn How a No-Nonsense IT Strategy Benefits Your ComBullet listpany:
Strategies to allocate your IT budget efficiently
Enhance cybersecurity defenses on a bButtonudget
Ensure your technology investments continue to serve your business as it grows
Looking to Switch?
© Copyright 2026 Big Water Tech. All Rights Reserved. Built in partnership with Tech Pro Marketing | Privacy Policy | Client Portal | Areas We Serve


