
Detroit's Trusted & Reliable IT Support Provider
For Small & Mid-Size Businesses
As a trusted MSP serving Southfield, Detroit, and the surrounding areas, Big Water Tech delivers expert business Outsourced IT Support, proactive cybersecurity, 24/7 help desk, and seamless BIGVoice VoIP phone systems. We take IT off your plate so you can focus on growing your business with confidence and peace of mind.
Schedule a Call
Schedule a 30-minute call to see if we are a good fit to help your business.
Your Neighborhood Technology Success partner
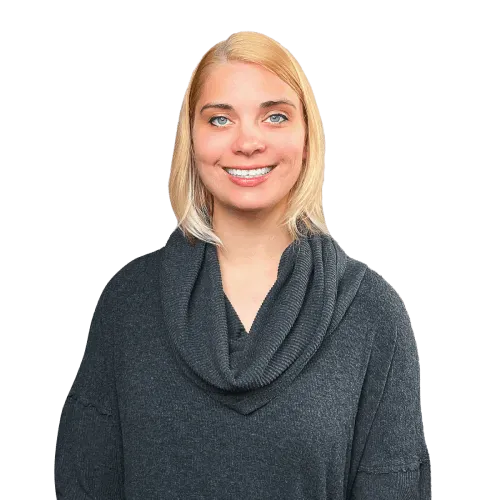
Tress Saunders
Client Success Coordinator
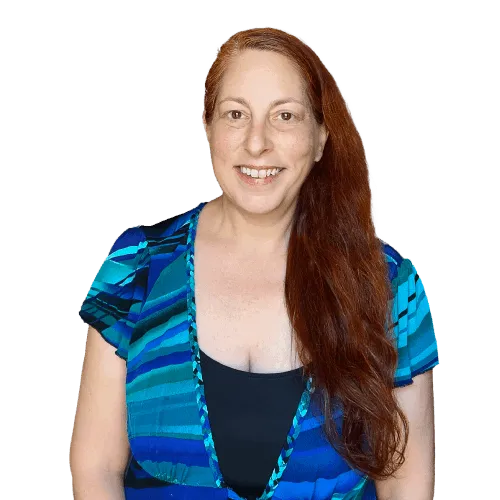
Jennifer Shubow
Senior Sales Executive
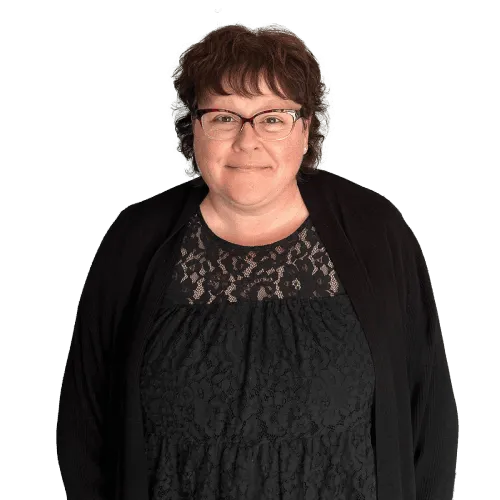
Beverly Ames
Carrier Services Manager
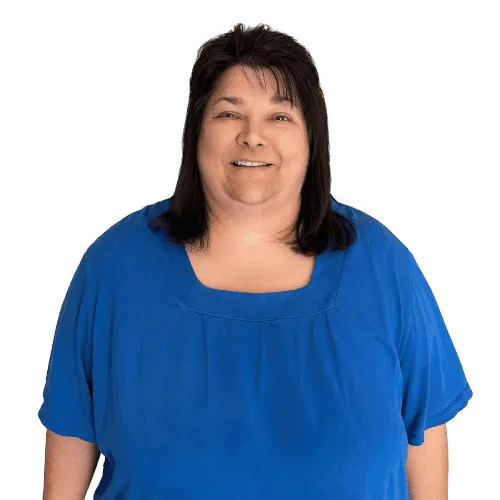
Lisa Sariol
Manager of Operations
Robert Shubow
President
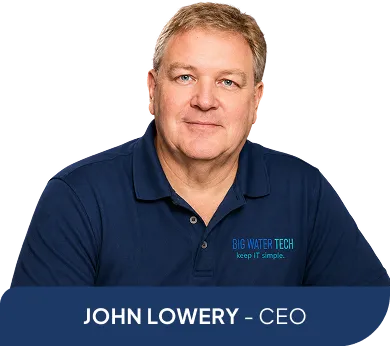
John Lowery
CEO
Marc Landau
IT Director
Bill Hickey
Client Services Manager
Glen Adams
Project Coordinator
Why Detroit Businesses Choose Big Water Technologies
Comprehensive IT Solutions
Big Water Technologies offers tailored business IT support solutions covering managed services, business phone systems, cybersecurity, cloud services, and more.
Security and Compliance Experts
You can rest assured knowing we're security and IT compliance experts. We are a Cyber AB Registered Practitioner for CMMC, helping Detroit businesses and government contractors meet federal cybersecurity requirements.
Exceptional Customer Service
Our team has been in the industry since the 1970s - allowing us to offer you informed, strategic insight while maintaining a high level of customer service.
Commitment to Client Success
You're far too busy to worry about technology and tech problems. That's why your success is our success. We make IT work for you - so you can drive growth, productivity, and have peace of mind.
Client Success Stories
We currently use Big Water for our managed phone service and they are great! We have had issue with managed phone service providers in the past but Jenn is super responsive when we have an issue or need a new line added or removed. I would not hesitate to recommend Big Water for managed phone services, low voltage or other technology needs!
COLLEEN BUDDE
Franchise Owner at Office Evolution Troy
Our Clients Say It Best
We’re proud to earn top marks from our clients through Crewhu’s customer feedback program. Every response helps us improve - and confirms that our team is making a real difference through responsive, friendly, and effective IT support. When our clients succeed, we succeed - and that’s what drives everything we do.
Is Your Technology Getting in the Way of Running Your Business?
You’re not alone, and it doesn’t have to be this complicated.
John Lowery
CEO, Big Water Tech
Big Water Tech is Here to Help Keep IT Simple with Our Reliable IT Support.
At BigWater Technologies, safeguarding the integrity and security of your IT system is non-negotiable. We're dedicated to optimizing your technology to enhance efficiency and power.
Feel like you’ve been down this road before?
If you've felt burned by managed services providers in the past, rest assured, we prioritize fostering lasting client relationships over maximizing profits. Our focus is on maximizing the potential of your current IT infrastructure while keeping costs in check – possibly even reducing them.
Contact us at (248) 220-7714 to kick-start crucial IT discussions tailored to businesses like yours. Let's redefine your IT experience together.
Schedule an Appointment Today
As Your Technology Success Partner,
We're Here to Help You Drive Growth With Our Services:

Simplified IT Management
BIGview offers proactive corporate IT support and IT management services of technology assets on a subscription basis.

VoIP & Hybrid Phone Systems
Desktop & Mobile App, as well as Service Management with flexible VoIP service.

Vendor Neutral Management
We provide a thorough needs assessment, available provider review, order management, issue management, and regular bill reviews.

Comprehensive Equipment Support
We take care of your network security, switching, WiFi, servers, computers, video conferencing, and more.

Installation & Support
Low voltage cabling, paging, and camera systems designed to fit the needs of your team.

Ongoing Evaluation and Planning
Stay focused on the success of your company with regular proactive business reviews.

Protect Your Business from Cyber Threats
Proactive monitoring, threat detection, and compliance-focused security solutions that safeguard your systems, data, and operations around the clock. Our BIGshare solution is HIPAA and PCI compliant, built for healthcare, legal, and financial services businesses.

Responsive User Assistance
Fast, reliable technical support that resolves user issues, reduces downtime, and keeps your team productive.

Empower Work, Anywhere, Anytime
Streamline collaboration, enhance productivity, and secure your business with expert Microsoft 365 setup, management, and ongoing support.

Scale Smarter, Operate Anywhere
Optimize performance, enhance flexibility, and reduce costs with secure, scalable cloud solutions tailored to your business needs.
What Clients Say About Us
Delivering exceptional customer service is at the heart of our IT management support services. Discover why businesses in Detroit rely on Big Water Tech for dependable IT and computer support.
Excellent Response
They have been our IT support for a number of years and we have always had excellent response for any issues we were having. We currently going through the process of setting us up for more Cyber Security and eliminating the use of a server. They are bringing us up to date with all our computer needs. Their staff is very helpful.

Sharon Pare
Great Experience
We have been using Big Water for managed Services and Support for the past 5-7 years and have had great experience with everything from New Purchase, to Support, to their proactiveness to help us protect our systems. I highly recommend this company for your IT needs.

Alan Borsen
Highly Recommend Their Services
The folks of Big Water are super supportive and helpful. And they thoroughly seem to enjoy find their customers huge savings. Their accurate in their communication and prompt to follow through with any promises. Highly recommend their services.
Korienna Cox
Amazing Company to Work With
Big Water Tech is an amazing company to work with. They are always available to handle any issues or problems that we are having in a timely manner.

Samantha Johnson
Always There
Thanks team! Your Big Water Technologies phone system helps me a lot to serve our customers. I also really appreciate that when I need your help, you are always there!

David Steighner
Solid Team of Professionals
BWT has done such a great job for us, it makes declining solicitor calls from competing companies easy work. BWT has a solid team of professionals that fully address any issue or concern that might arise during the daily course of our business. We are very satisfied with their service and intend to continue our relationship far into the future.

Adam Cowan
Quick to Respond
Big Water Technologies/IT Support Service is a great company! They are quick to respond and to get our questions answered. They are quick to come to our office and accurately do the job we need. If you need a great technology company for all your IT and Phone services - Call Big Water Technologies!

Cathy Bouford
Managing Your Security Has Never Been Simpler

Discover Your Cyber Score
Start by assessing your Cyber Score to understand your business’s online security. This score provides clarity, replacing uncertainty with insight, so you know exactly where you stand and what needs improvement.

Create Your Cyber Roadmap
Use your Cyber Score to develop a clear, actionable Cyber Roadmap. This plan highlights vulnerabilities and provides precise steps to strengthen your security, saving you time and resources. Schedule a meeting with Big Water Tech so we can help you create a clear, strategic path to cyber resilience.

Enhance Your Security
Put your Roadmap into action with a step-by-step approach to stronger protection. Demonstrate your commitment to safeguarding customer data while equipping your IT team with a focused, cost-effective security strategy.
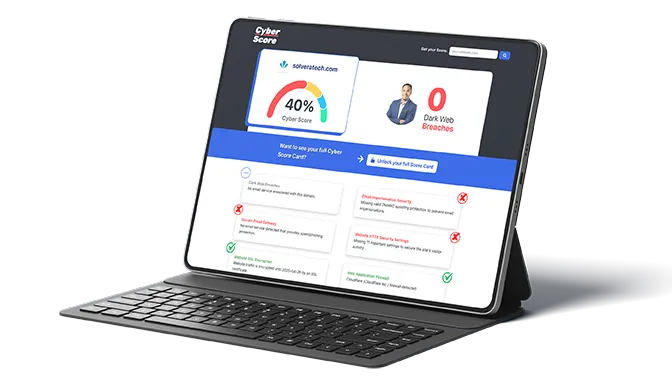
Want to see your Free Cybersecurity Score?
Get it in 30 seconds!
Stay Ahead with Big Water Tech Insights
IT Wisdom Worth Reading for Growing Businesses
Our blog shares practical guidance, expert takes, and real-world lessons drawn from the front lines of IT services & solutions. Stay informed, stay protected, and make smarter decisions for your business or organization.
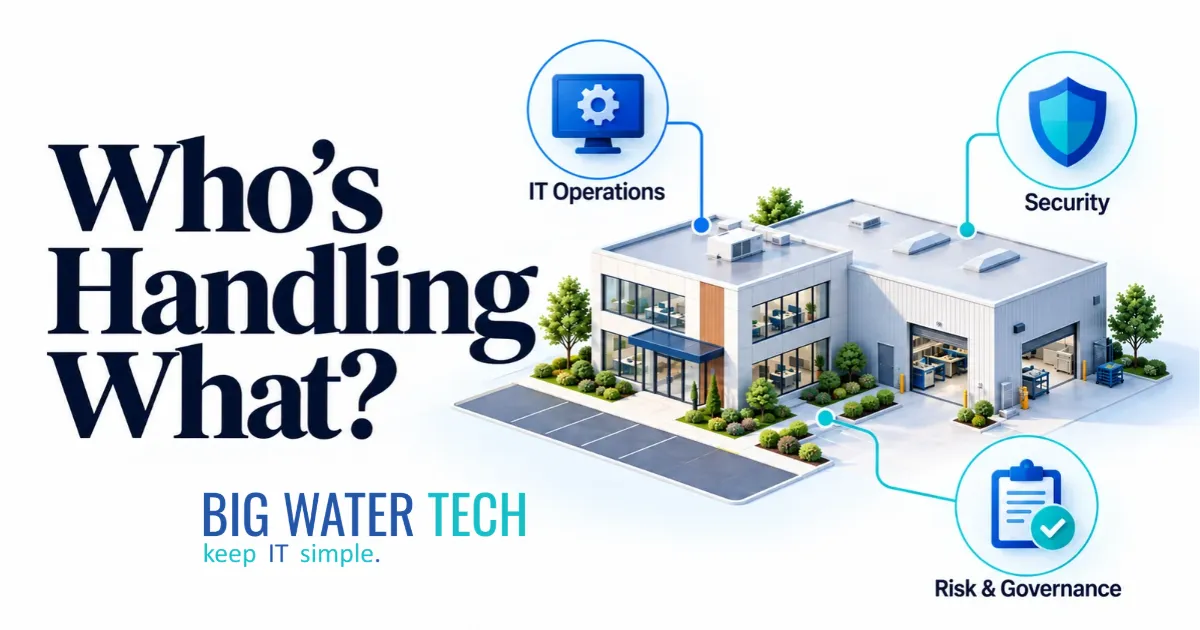
Are You Paying Twice for IT, or Leaving Something Uncovered?
“We already have an IT company. Why do we need someone else?”
It’s a fair question when someone recommends a security assessment or a virtual Chief Information Security Officer, usually called a vCISO. You’re already paying for IT support, and you expect that relationship to include protecting the business. Then someone introduces an MSSP or a governance, risk, and compliance service, and it sounds like another invoice for work you thought was covered.
There is overlap between these services. There are also responsibilities that get missed because everyone assumes they belong to someone else. Before adding another service, you need to understand what your current agreement covers and what the additional work will accomplish.
What is the difference between an MSP, an MSSP, and a GRC service?
An MSP manages technology operations. An MSSP specializes in operating cybersecurity services. A GRC service helps leadership manage risk and meet business obligations. One provider can perform several of these functions, depending on its capabilities and your agreement.
The leadership roles fit within that picture. A vCIO guides technology decisions around business needs. A vCISO leads the cybersecurity program and helps management make informed security decisions.
Service or role | Primary focus | Example of the work |
|---|---|---|
MSP: Managed Service Provider | Supporting and managing business technology | Maintaining systems and resolving employee technology problems |
MSSP: Managed Security Service Provider | Operating cybersecurity services | Investigating suspicious activity and taking authorized response actions |
vCIO: Virtual Chief Information Officer | Technology direction and investment | Planning technology requirements and spending for another location |
vCISO: Virtual Chief Information Security Officer | Cybersecurity leadership | Establishing security priorities and overseeing progress |
GRC: Governance, Risk, and Compliance | Risk oversight and business requirements | Maintaining a risk register and documenting evidence for customer security obligations |
These are typical responsibilities. The label on a proposal doesn’t establish the scope of the service, and having one of these services doesn’t automatically cover the others.
What should your MSP be responsible for?
Your MSP should manage the technology and support responsibilities defined in your agreement, including the security services you have purchased. That generally includes ongoing system administration and employee support, but coverage varies considerably.
CISA recommends that providers and customers clearly identify ownership of security responsibilities in their contracts. That matters because an assumption about coverage is difficult to resolve while an incident is underway. www.cisa.gov
For a Michigan law firm, the MSP relationship might include Microsoft 365 administration and coordination with the document management vendor. For a manufacturer, it might include maintaining the network that connects office systems to production applications.
I expect a good MSP to understand how those systems affect the business. If an aging server supports your scheduling application, a replacement recommendation should arrive early enough for you to plan the spending and disruption.
That’s where vCIO involvement matters. The vCIO works with leadership on technology direction, including whether the current environment will support the company’s plans. A quarterly equipment report alone doesn’t provide that leadership.
Does having an MSP mean you also need an MSSP?
No. You need appropriate security capabilities, but those capabilities can already be part of your MSP relationship. Some MSPs operate security services themselves. Others use specialist partners to deliver them.
An MSSP focuses on services such as security monitoring and alert investigation. Its agreement determines whether it also contains threats or performs broader incident response.
The practical question is what happens after an alert appears. If suspicious activity occurs at 2 a.m., does someone investigate immediately? Can they isolate an affected computer without waiting for your office to open?
There’s a substantial difference between receiving a notification and having someone authorized to act. “Security monitoring included” doesn’t explain which service you bought.
Before signing another contract, ask your MSP to explain its existing coverage, including any security partners and the limits of their response authority. You need to understand where responsibility passes from one team to another.
How is a vCIO different from a vCISO?
A vCIO guides technology decisions across the business. A vCISO leads the cybersecurity program and advises management on security risk. Both roles require planning and follow-through.
Your vCIO helps evaluate whether your technology supports business operations and future investment. Your vCISO establishes security priorities and oversees whether the organization addresses them.
Suppose a manufacturer plans to acquire another company. The vCIO evaluates how the technology environments will fit together and what integration will cost. The vCISO evaluates the security exposure involved in connecting them and establishes the conditions for doing so.
Calling the vCIO a doer and the vCISO a planner gives part of the picture, but it leaves too much out. A vCIO needs to plan beyond the next project, and a vCISO needs to ensure recommendations lead to completed work.
These roles overlap because technology decisions have security consequences. They still need defined responsibilities, even when the same provider supplies both services.
What does a GRC service add to managed IT?
A GRC service turns risk decisions and business obligations into an ongoing program with assigned ownership and documented evidence. It connects what leadership has agreed to do with what actually happens.
For a manufacturer, the trigger is often a customer contract with security requirements. For a law firm, it might be a client’s vendor questionnaire asking for documented access reviews or evidence of an incident response exercise.
Someone needs to determine what each requirement means for the business, identify gaps, and assign the work. Someone also needs to track completion and keep the supporting evidence current.
A vCISO can lead that program through a GRC service. Technical implementation often remains with the MSP or internal IT staff, while management retains authority over business risk decisions.
NIST’s Cybersecurity Framework 2.0 includes governance because cybersecurity requires leadership decisions about accountability and acceptable risk. Those responsibilities exist alongside technical protection and response. nvlpubs.nist.gov
How do these services work together when a critical vulnerability is found?
Consider a manufacturer whose security scan identifies a critical vulnerability in the server supporting its production application. The software vendor requires testing before the update can be installed, and remediation will require downtime during a busy production week.
The security provider validates the finding and investigates whether there are signs of exploitation. The MSP works with the application vendor to establish a safe remediation process.
The vCIO helps operations understand the downtime and scheduling implications. The vCISO evaluates the exposure during the delay and works with the technical teams on temporary safeguards.
Management then decides whether the proposed delay is acceptable, based on the consequences of both acting and waiting. The GRC process records the decision, assigns a deadline, and tracks the evidence that remediation was completed.
One organization can handle several parts of that work. What matters is that the finding moves through to a verified resolution. A critical item sitting on a monthly report doesn’t establish that anyone owns it.
When are you paying twice for the same IT service?
Duplicate spending occurs when you pay for substantially the same work without a clear additional benefit. Two providers supplying similar monitoring across the same systems deserves examination.
Separate fees don’t automatically mean duplication. A provider operating security tools and a vCISO overseeing the security program perform different work. So do an MSP implementing access controls and a GRC team verifying that those controls satisfy an agreed requirement.
Ask each provider to identify its deliverables and explain how they connect. If both claim to “manage security,” they should be able to describe their responsibilities without leaving you to sort them out.
Additional oversight should produce decisions and completed work. Another report repeating findings you already know about needs a better explanation.
When does a small business need vCISO or GRC support?
Dedicated vCISO or GRC support becomes useful when security obligations exceed the time or experience available within the business. Employee count alone doesn’t settle the question.
That often happens when customer contracts introduce requirements that nobody currently owns. It also happens when internal IT staff understand the technical problems but need leadership support to resolve competing priorities.
A 25-person firm handling sensitive client information can have significant obligations. A larger company with established internal leadership might need targeted assistance with an assessment or an incident response exercise.
I’d look at the decisions going unmade and the work going unfinished before choosing a service level. An approaching audit creates urgency, but unresolved customer commitments are a reason to act earlier.
What should you ask before adding another IT or security service?
Start with your existing agreements and ask:
Who investigates security alerts, including after hours?
What response actions are they authorized to take?
Who owns remediation when several vendors are involved?
Who maintains policies and evidence for customer requirements?
Who presents unresolved risks to management?
Who verifies that corrective work was completed?
Put the answers in a responsibility matrix that includes internal staff and relevant software vendors. Each responsibility needs a named owner, with an escalation process for work that stalls.
You should also know what falls outside the agreement. If incident response is separately billed or compliance documentation remains your responsibility, that needs to be understood before you depend on the service.
How does Strata Advisory Group fit with Big Water Technologies?
Strata Advisory Group is Big Water Technologies’ GRC service, providing dedicated vCISO leadership and support for governance, risk, and compliance.
BWT’s managed IT relationship includes vCIO guidance alongside ongoing technology management and support. That helps clients plan technology investments around business needs.
Strata adds dedicated security leadership and risk oversight. Its work includes helping organizations establish security priorities and document risk decisions, along with preparing for customer or audit requirements. Strata coordinates with whoever handles technical implementation, whether that’s BWT, another provider, or internal IT.
For a manufacturer facing new customer security obligations, that means connecting the contractual requirements to assigned work and evidence of completion. For a professional services firm, it means giving leadership a clear view of its exposure and the decisions that need attention.
I wouldn’t recommend adding GRC services simply because your business reached a certain employee count. I would want to understand which responsibilities need attention and whether your existing team has the time and experience to cover them.
If you’re unsure what you’re paying for, ask Big Water Technologies to review your current coverage before adding another agreement. You should be able to see what each service covers and what still requires a decision from you. Paying someone to advise the business doesn’t transfer management’s accountability for the risk it accepts.
Frequently Asked Questions
What does an MSP (Managed Services Provider) do?
An MSP proactively monitors, maintains, and secures your IT environment so your business runs smoothly. Big Water Tech handles backups, patching, help desk support, and cloud services, giving you predictable costs, faster response times, and a reliable technology success partner focused on your success across Detroit.
Why choose a local MSP in Southfield and Detroit?
Choosing a local MSP means faster on‑site support, better understanding of regional business needs, and more personalized service. Big Water Technologies is a Southfield‑based Technology Success Partner that serves Detroit, offering managed IT services, cloud solutions, VoIP, and IT consulting that align with your local operations and growth goals.
How does Big Water Technologies’ BIGVoice VoIP phone system work?
Big Water Technologies’ BIGVoice business VoIP phone system uses the internet to deliver voice calls, conferencing, and advanced features across your office and remote teams. It integrates with your existing IT environment, scales with your business, and reduces phone‑line costs while improving reliability and communication tools for your Metro Detroit‑area organization.
How does Big Water Tech approach cybersecurity?
Big Water Tech takes a proactive, layered approach to cybersecurity, combining threat monitoring, endpoint protection, secure backups, and employee training. We assess your unique risks, implement tailored defenses, and continuously update your security posture to protect data, systems, and compliance across your Detroit organization.
What are the benefits of outsourcing IT support and services?
Outsourcing IT support gives you access to expert resources without the overhead of an in‑house team. With Big Water Tech, you gain faster response times, reliable help desk support, scalable cloud solutions, and stronger cybersecurity, so your Detroit business stays agile, secure, and focused on growth.
Take IT Off Your Plate...
Spend less time on IT problems and more time growing your business. Let’s get to know each other and determine how our partnership could grow. With us as your trusted MSP on your side, you can develop a strong barrier against cybercrime, stronger communication strategies, and a better technology plan for the future.
Call (248) 220-7714 today or fill out the form below to schedule your appointment. We’re ready to jumpstart your IT journey.
Looking to Switch?
© Copyright 2026 Big Water Tech. All Rights Reserved. Built in partnership with Tech Pro Marketing | Privacy Policy | Client Portal | Areas We Serve


